Kaushal
Stablecoin Payment Infrastructure
Overview


Want to work together? (Currently Open to Work)
Book a free call instantly.
About
I am a senior engineer building stablecoin payment infrastructure and the systems that let autonomous AI agents move money safely. My work sits where payment rails, distributed systems, and agentic software meet. I design the control plane, the settlement path, and the evaluation harness that proves the system holds up when things go wrong.
- Stablecoin payment rails in production: As founding engineer at PayZoll I built a multi-tenant Stellar Disbursement Platform with isolated tenants, hot wallets, and rate limits per organization. Just-in-time USD to USDC/EUR/XLM conversion and Xflow virtual accounts carry cross-border USDC-to-INR settlement. I raised throughput ~100x (2 to 200 tx/s) by using Soroban's authorization-tree model to get past SDP's 8-channel-account limit. It runs on Stellar mainnet, processed up to $11K/month at peak, and was backed by a $100K Stellar Community Fund grant.
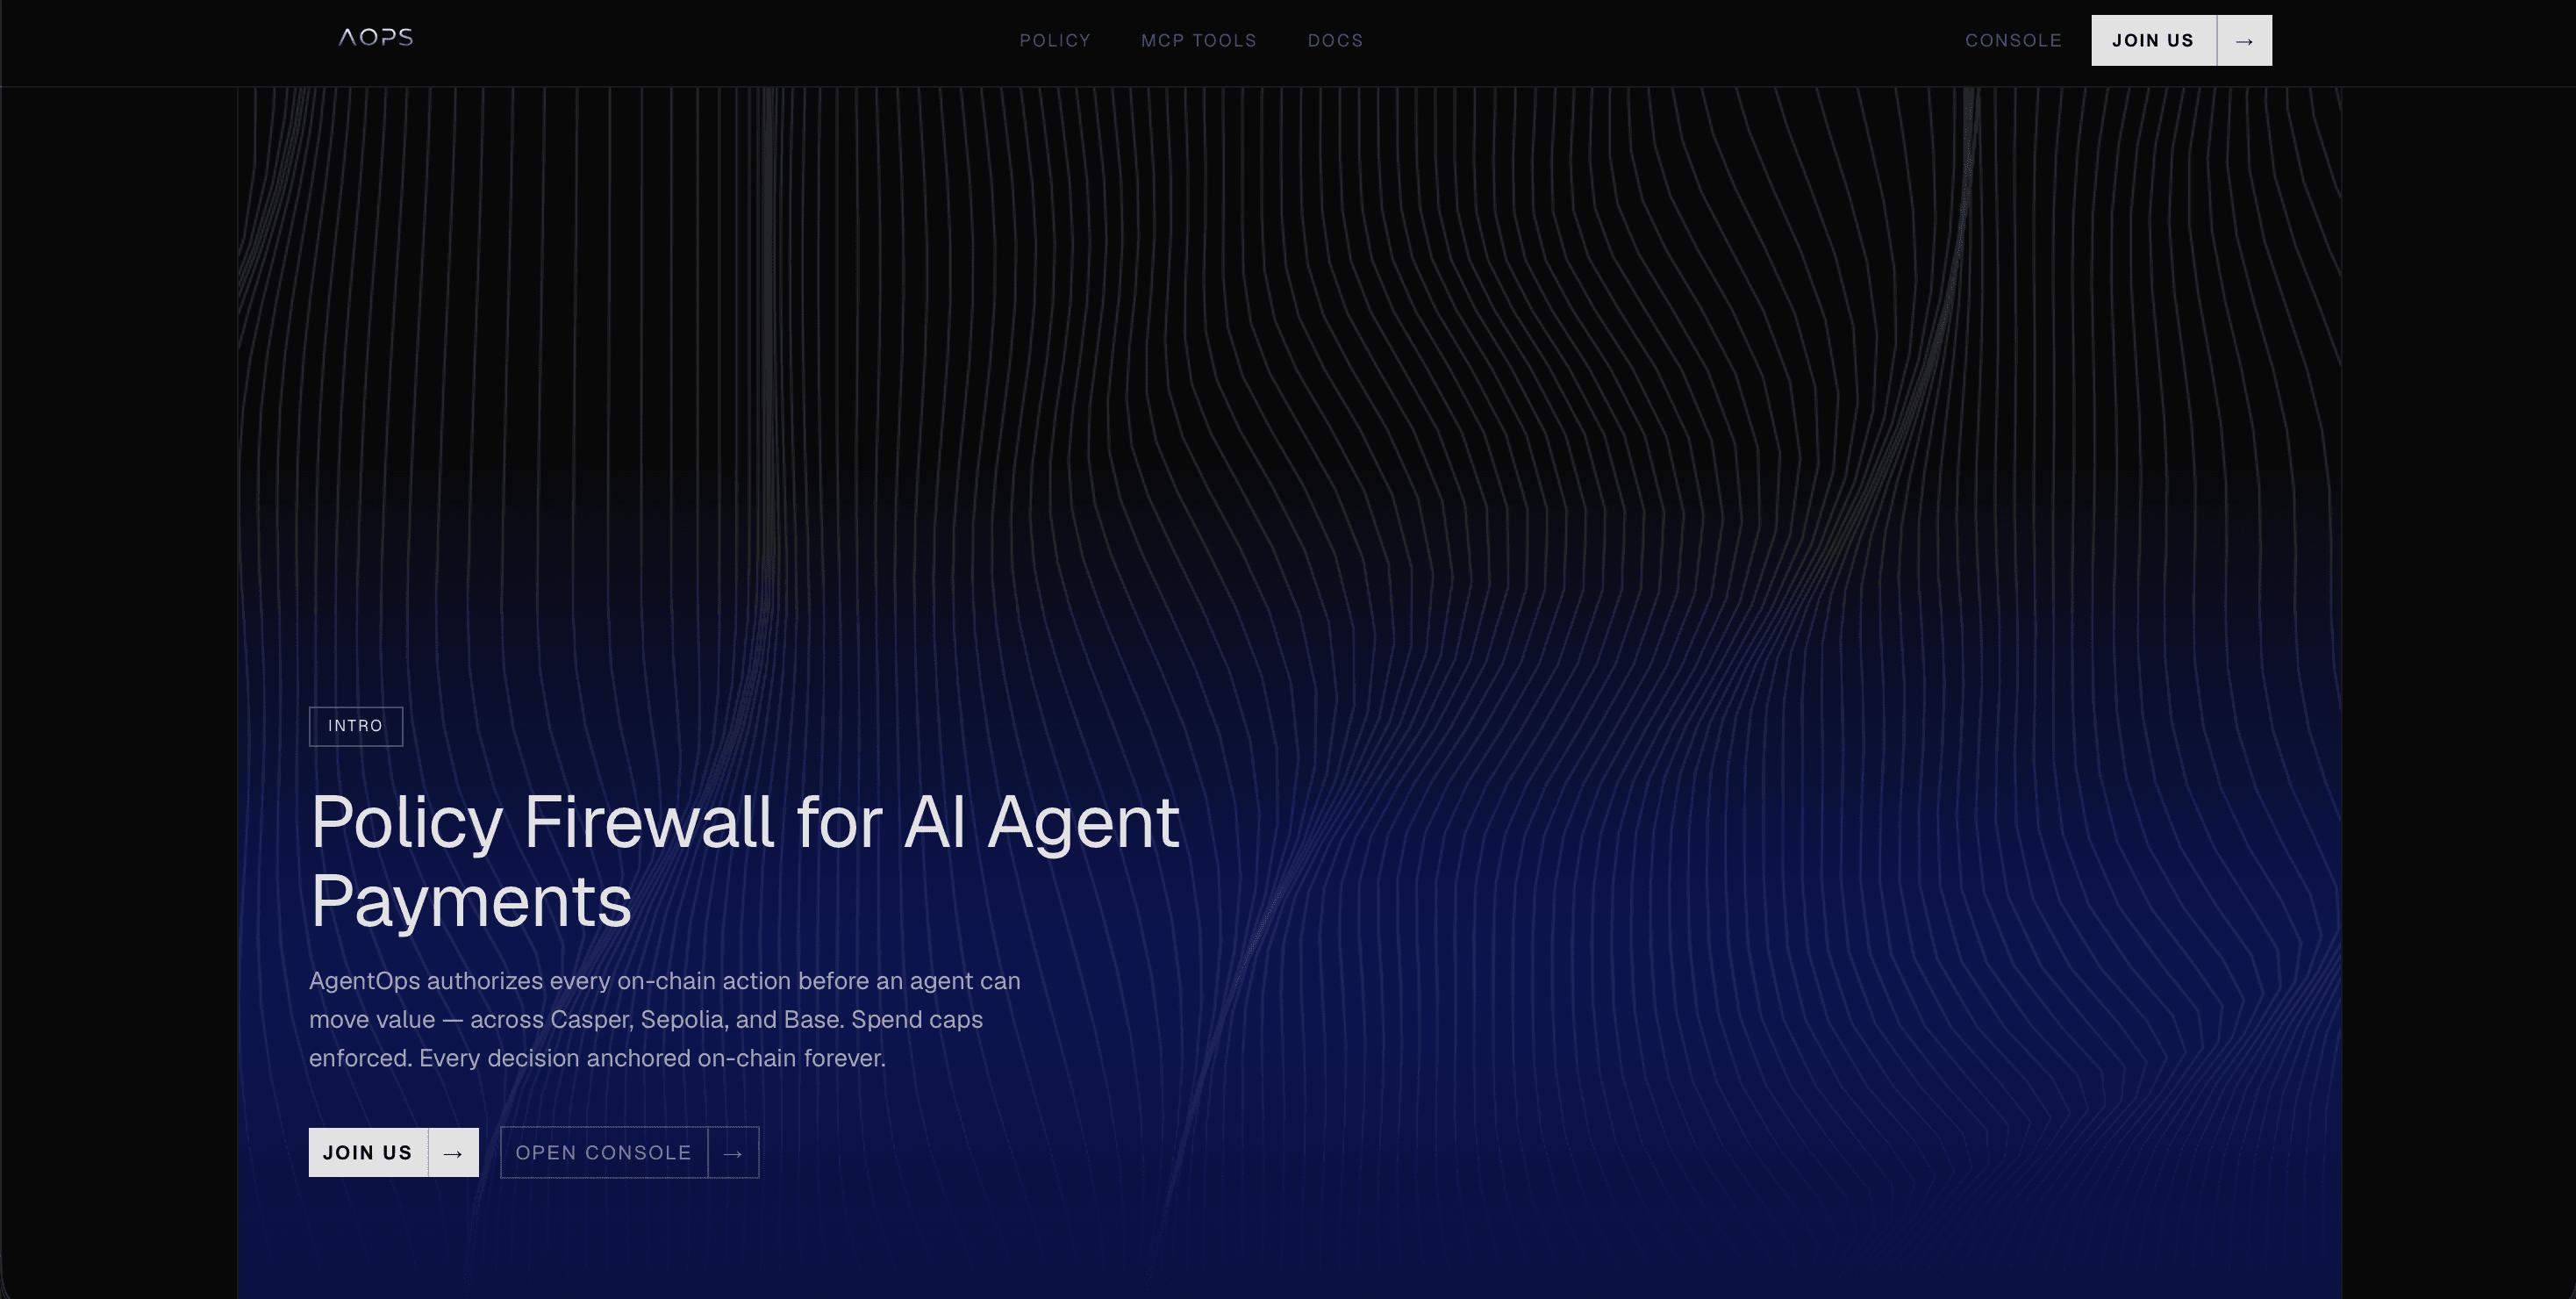
- Agentic commerce and payment governance: AgentOps is a pre-execution financial control plane for AI agents. Every payment passes per-agent wallets, org budgets, spend caps, and human approval gates before it can settle. A single multi-rail abstraction covers x402 for external payments and Permit2 for intra-fleet transfers, exposed through a hosted MCP server and SDK, and every decision is written to a hash-chained audit log.
- Agent harnesses and evals: I treat agents as untrusted actors and test them that way. My evaluation workflows replay execution traces against adversarial scenarios: overspending, prompt-injected payment requests, retry storms, and cross-agent budget contention. On live Arc testnet the policy engine rejected 100% of $25 attempts against a $20 USDC wallet and still settled valid $5 payments. Failed balance reads never turn into a decision to spend.
- System design and microservices: At Noketa I split a monolith into independently deployable services (Public API, Control Plane, Inbound Lambda, SMTP/IMAP) inside a Bun/Turborepo monorepo. A common channel abstraction lets new integrations ship as adapters instead of rewrites. At TheOpenAssets I kept ~20 domain modules (issuance, compliance, markets, yield, leverage, solvency) independently maintainable inside one deployable system, with idempotent event indexing across 6 chains.
- Compliance by construction: ERC-3643 identity-bound issuance, consent and suppression enforcement, tenant-isolated credentials, KMS-managed keys, and audit trails are part of the architecture from day one, not added before an audit.
- Smart contract depth: Solidity and Soroban/Rust across escrow (ERC-8183), vaults, PT/YT yield tokenization, and RWA compliance. 7x hackathon winner and BNB Chain Martian.
Featured Builds
View all buildsGitHub Contributions
Stack


Blog(1)
Experience
Achievement: Finalist at CasperHacks; selected for Arc accelerator review from 500 projects.
- Architected a pre-execution financial control plane for autonomous AI agents. Per-agent wallets, org budgets, spend caps, and human approval gates are enforced before any value moves, for both external x402 payments and intra-fleet transfers. Hash-chained audit logs and isolated settlement credentials back every decision.
- Designed a multi-rail payment abstraction: x402 for external payments, Permit2 for intra-fleet transfers, and cross-chain settlement to Base, all exposed through one hosted MCP server and runtime SDK that Claude/Cursor agents and any other agent runtime can use.
- Proved policy enforcement on live Arc testnet: rejected 100% of $25 payment attempts against a $20 USDC wallet while settling valid $5 payments, checked against both funded balances and organizational policy.
- Built a hierarchical 5-agent fleet (Orchestrator, DataFetcher, Analyst, Writer, SeniorReviewer) under a shared org budget to exercise budget contention and runtime overspend prevention.
- Built an agent evaluation harness with replayable execution traces and adversarial scenarios: overspending, prompt-injected payment requests, retry storms, and cross-agent budget contention.
- Hardened live-chain execution: bounded retries (6 attempts, 400 ms backoff) for flaky Arc RPC balance reads, fixes for Permit2 nonce-reuse and settlement bugs, and a fail-closed rule so a failed balance read can never lead to a spend.
- Found and publicly reported a Circle Developer-Controlled Wallets bug that rejected externally funded Base Sepolia wallets for insufficient ETH despite sufficient on-chain funds.
- Deployed a vendored ERC-8183 escrow on Arc and Base Sepolia, found a budget-mismatch path in a stale contract build, and pinned verified builds in the deploy process.
- x402
- Permit2
- MCP
- Agent Evals
- Policy Engine
- HITL Approvals
- Multi-Agent Orchestration
- USDC
- Circle
- Arc
- Base
- ERC-8183
- TypeScript
Impact: Took Noketa from MVP to production-ready infrastructure and onboarded 7 SaaS founders onto the platform.
- Split a monolith into independently deployable microservices (Public API, Control Plane, Inbound Lambda, and an SMTP/IMAP mail server) inside a Bun/Turborepo monorepo, so teams could build in parallel and ship channels faster.
- Built a unified omnichannel messaging platform across 5 channels (Email, SMS, WhatsApp, Push, Instagram) on a common channel abstraction, so new integrations ship as adapters instead of platform rewrites.
- Integrated AWS End User Messaging, SES/SNS, and Meta Graph APIs for outbound delivery, webhook-driven bounce and complaint processing, and automated STOP/HELP handling with consent and suppression enforcement.
- Designed a multi-agent GTM automation system for outreach, campaigns, and workflows using supervisor-worker orchestration and human-in-the-loop approval gates, cutting LLM token costs by 15%.
- Reduced production provisioning and cutover to a single command that combines Terraform, Infisical, and Neon database branching, with mock-mode testing across all 5 channels.
- Shipped compliance-focused SMS (MMS/RCS, quiet hours, consent management, keyword preferences) that the internal marketing team now uses for live campaigns.
- Microservices
- Turborepo
- Bun
- Hono
- Next.js
- Terraform
- Neon
- Drizzle ORM
- Better Auth
- Redis
- Stripe
- AWS
- Meta Graph API
- Multi-Agent Systems
Impact: Live on Stellar Soroban mainnet; processed up to $11K/month at peak; onboarded HackQuest as a paying enterprise client; secured a $100K Stellar Community Fund grant.
- Built a multi-tenant Stellar Disbursement Platform (SDP) that gives each organization an isolated tenant with its own hot wallets, assets, payroll records, and API rate limits.
- Engineered the Node.js/Express orchestration layer: tenant-level login and MFA, Redis-cached SDP JWTs (15-minute TTL), and encrypted in-memory credential caching for seamless re-authentication.
- Scaled payroll throughput ~100x, from ~2 to ~200 tx/s, getting past SDP's 8-channel-account limit by using Soroban's authorization-tree model for parallel contract calls.
- Implemented just-in-time conversion of USD salaries to USDC, EUR, and XLM using CoinGecko rates cached in Redis, for rapid on-chain disbursement.
- Enabled cross-border USDC-to-INR payments by integrating Xflow APIs and virtual accounts with Stellar, giving near-instant on-chain settlement with less reliance on traditional banking rails.
- Automated bulk payroll with CSV uploads, background workers, and disbursement-status polling, plus org-scoped SSE from PostgreSQL that powers real-time admin dashboards.
- Built the observability and ops stack: OpenTelemetry, Sentry, PostHog, PM2, and Docker on GCP (GCE, Cloud Build) behind Cloudflare Tunnel.
- Stellar
- Soroban
- SDP
- USDC
- Cross-border Payments
- Node.js
- Express
- PostgreSQL
- Redis
- JWT / MFA
- OpenTelemetry
- GCP
- Docker
Achievement: Won at OneChain ($3,000), U2U ($4,000), and Mantle ($2,000). Secured an LOI from Triambi Solar to explore tokenizing solar project assets and revenue streams.
- Architected a modular backend of ~20 domain modules (issuance, compliance, markets, yield, leverage, solvency) shipped as one deployable system: simple to operate, with each domain still independently maintainable.
- Engineered end-to-end ERC-3643 issuance across 17 Solidity contracts, covering identity verification, compliance enforcement, primary issuance, and secondary-market settlement.
- Designed a unified multi-chain integration layer across Mantle, HashKey, Creditcoin, BNB Chain, Arbitrum, and Stellar/Soroban that handles chain-specific transactions, wallets, events, payments, and signatures without duplicating business logic.
- Built an on-chain event indexing pipeline across 9 contracts with background workers and idempotent handlers, keeping data about 8 seconds fresh with rate-limit-aware polling and recovery for missed events.
- Implemented liquidation monitoring that checks health factors every 60 s and liquidates below 115%, plus cross-chain credit scoring (60% platform history, 40% Creditcoin history) with fallbacks and 55-75% LTV limits.
- Set engineering standards: shared type definitions, module-level architecture docs, and end-to-end tests of critical financial flows such as deposit-to-borrow.
- NestJS
- TypeScript
- Solidity
- ERC-3643
- RWA
- MongoDB
- Redis
- BullMQ
- SSE
- Rust
- Stellar
- Mantle
- Foundry
Achievement: Designed and shipped the protocol in 48 hours, taking 3rd place ($1,000) at the Tezos x Etherlink AI Hackathon.
- Built a non-custodial XTZ vault that mints ERC-20 shares 1:1 against deposits, with pro-rata redemption and yield distribution made replay-safe by unique event IDs.
- Designed principal/yield tokenization (PT/YT at 1:1) with maturity-based loss absorption, so yield absorbs staking losses before principal.
- Engineered isolated risk pools (separate vault, oracle, competition, and AMM deployments) for 6% delegation yield and 18% slashing-exposed yield, so losses in one pool can't touch the other's reserves.
- Built an on-chain forecasting competition where bonded agents predict baker performance, with accuracy-based settlement, 5% bond slashing, and keccak256 commitments of off-chain agent reasoning.
- Optimized yield accounting with a monotonic 1e18-scaled oracle index, capped 5% updates, lazy per-holder accrual, and a time-decay AMM that converges to face value at maturity.
- Solidity
- Etherlink
- OpenZeppelin
- wagmi
- AI Agents
- AMM
- Yield Tokenization
- Node.js
- Docker
Achievement: Submitted to the Stellar Community Fund (SCF); received strong reviews from SCF reviewers.
- Built the client for a privacy-first payments protocol on Stellar, with two products: batch payroll, where one signature pays up to 80 people, and private payments, where withdrawals can't be linked back to the payer.
- Designed layered encryption in the browser so payment instructions pass through the relayer without it ever seeing who is being paid, and the payer's identity never appears on-chain.
- Kept the backend blind to user addresses by hashing identities on the client before anything leaves the browser.
- Turned a complex multi-contract payout into a single wallet approval, with every transaction simulated and costed before the user signs.
- Stellar
- Soroban
- Freighter
- Applied Cryptography
- Web Crypto
- Privacy
- Next.js
- Zustand
Education
- C++
- Java
- Python
- DSA
- Systems Design
- Distributed Systems
- Software Engineering
- Blockchain
Issues I Resolved(1)
Issue
A junior developer’s local app was returning ERR_CONNECTION_REFUSED when accessed through https://app.xyz.dev.
Root Cause
The application itself was running correctly on localhost:4137. However, Portless was running in HTTP mode on port 1355 instead of serving HTTPS on port 443.
Since .dev domains are HSTS-preloaded, the browser automatically enforces HTTPS. It therefore tried to connect to:
https://app.xyz.dev → 127.0.0.1:443
but nothing was listening on port 443, resulting in ERR_CONNECTION_REFUSED.
Resolution
I restarted the Portless proxy with HTTPS support and configured it to use the xyz.dev TLD:
bunx portless proxy stop
bunx portless proxy start --tld xyz.dev
bunx portless trust
bunx portless doctor
The proxy was then able to bind to port 443 with elevated permissions.
Result
The local application became accessible through https://app.xyz.dev.
The issue was not with the application or Vite server; it was caused by the local HTTPS proxy configuration and .dev HSTS enforcement.
- HTTPS
- HSTS
- Portless
- Vite